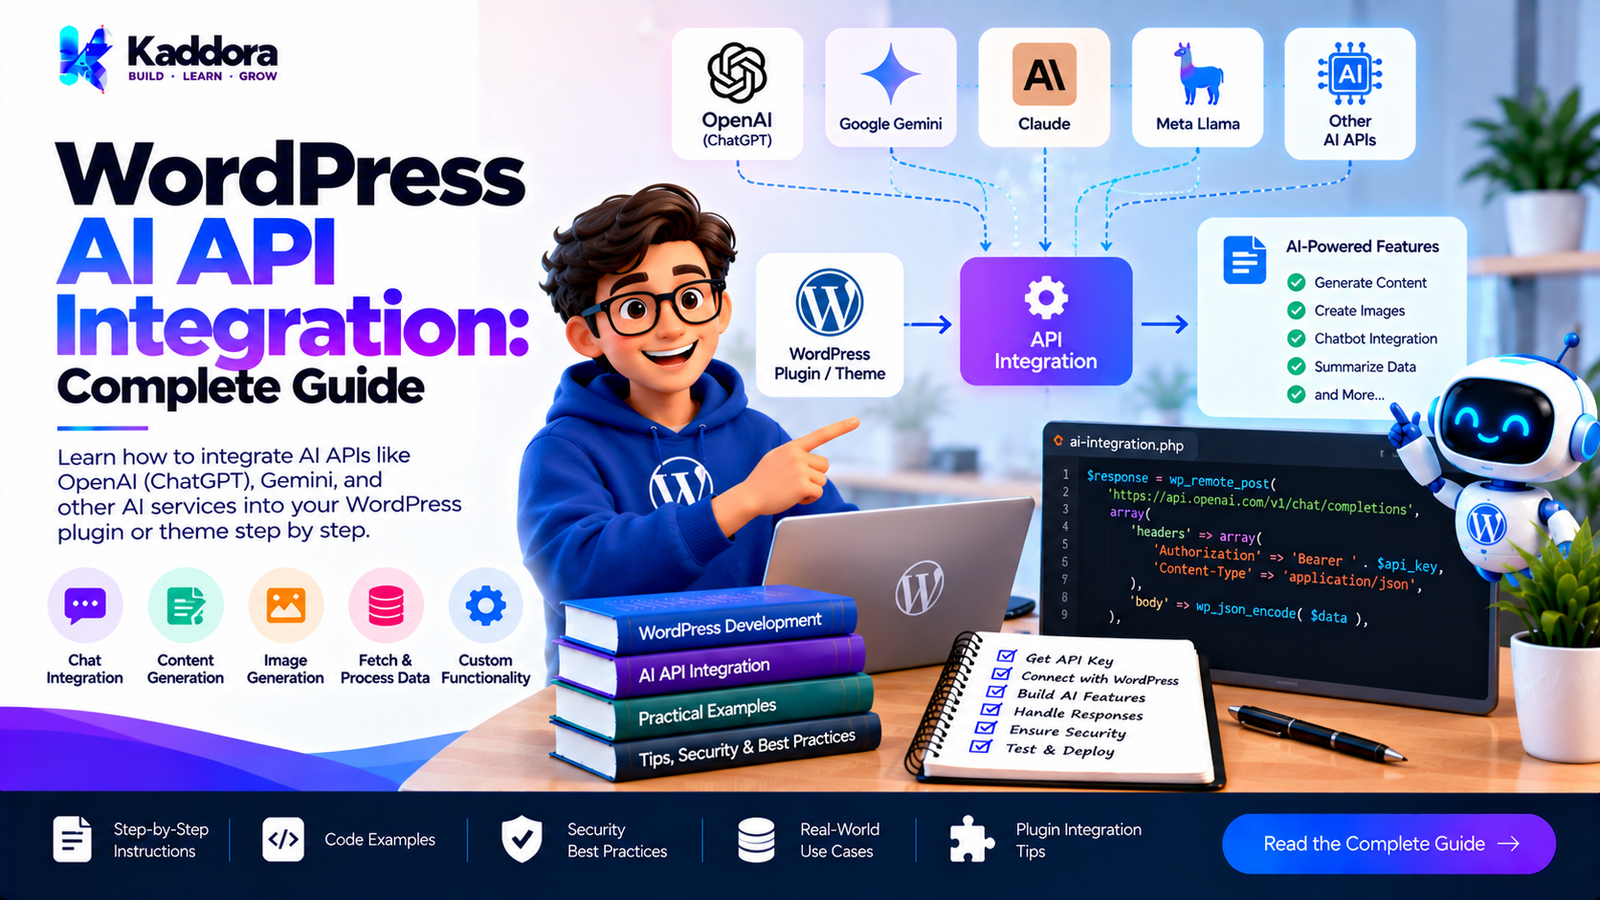
WordPress AI API Integration: Complete Guide
Introduction
Artificial intelligence can add powerful capabilities to WordPress websites and plugins.
With an AI API integration, a WordPress plugin can communicate with an external AI service to generate content, analyze information, answer questions, summarize documents, create recommendations, process images, improve search, and automate repetitive workflows.
A basic integration may appear simple:
WordPress ↓ AI API ↓ AI Response
However, a production-ready integration requires more than sending an HTTP request.
A reliable WordPress AI API integration should consider:
Authentication
API credentials
Request validation
Prompt construction
HTTP requests
Response parsing
Response validation
Error handling
Rate limiting
Caching
API costs
Privacy
Security
Background processing
User experience
This guide explains how to integrate an AI API with WordPress and how to design the integration so it can remain secure, maintainable, and scalable.
What Is WordPress AI API Integration?
WordPress AI API integration is the process of connecting a WordPress website or plugin to an external artificial intelligence service through an API.
The API acts as a communication layer between WordPress and the AI provider.
A typical workflow looks like:
WordPress User ↓ WordPress Plugin ↓ AI API Request ↓ AI Provider ↓ AI Response ↓ WordPress Plugin ↓ User
The AI provider handles model processing while the WordPress plugin manages the website-specific workflow.
Why Integrate an AI API With WordPress?
WordPress provides an excellent platform for building content and business workflows, while AI can add intelligent processing.
Combining the two can enable features such as:
AI content generation
AI writing assistance
AI SEO analysis
AI chatbots
Customer support
Product descriptions
Product recommendations
Image analysis
Alt text generation
Semantic search
Translation
Summarization
Data extraction
Lead qualification
Workflow automation
The best integrations solve a specific user problem instead of adding AI simply for the sake of adding it.
How a WordPress AI API Integration Works
A typical architecture is:
User Interface ↓ WordPress Plugin ↓ Request Handler ↓ Validation ↓ AI Service ↓ API Client ↓ AI Provider ↓ Response ↓ Validation ↓ WordPress Feature
Supporting components may include:
Cache Queue Logger Settings Rate Limiter Database
Not every plugin needs every component.
Step 1: Define the AI Use Case
Before choosing an API, determine what the integration should do.
For example:
Content Generation
Topic ↓ AI API ↓ Article Draft
Product Description
WooCommerce Product ↓ AI API ↓ Product Description
Customer Support
Customer Question ↓ Knowledge ↓ AI API ↓ Answer
Image Alt Text
Image ↓ AI Vision API ↓ Alt Text
Defining the use case first helps determine the correct architecture.
Step 2: Choose an AI Provider
Different AI providers offer different capabilities, models, pricing structures, limits, and APIs.
When selecting a provider, consider:
API capabilities
Supported models
Pricing
Rate limits
Input types
Output formats
Availability
Authentication
Privacy policies
Documentation
Developer tooling
The provider should match the requirements of your plugin.
Step 3: Understand the Provider API
Before writing the WordPress integration, understand the provider's current API documentation.
Review:
Authentication method
Endpoint
HTTP method
Request structure
Required parameters
Response structure
Error responses
Rate limits
Timeout behavior
Do not assume that every AI provider uses the same request or response format.
Step 4: Keep API Credentials Server-Side
Private API credentials should not be exposed to website visitors.
Avoid:
Browser ↓ Private API Key ↓ AI Provider
Instead:
Browser ↓ WordPress ↓ Plugin ↓ AI Provider
The WordPress plugin acts as the server-side integration layer.
Step 5: Create a WordPress Settings Page
An AI plugin will often need a settings page.
Possible settings include:
AI Provider API Key Model Maximum Output Feature Status Request Limits Logging
For example:
AI Settings Provider [ AI Provider ] API Key [ ********************** ] Model [ Selected Model ] Enable AI [ Yes ] [Save Settings]
Only users with appropriate WordPress capabilities should be allowed to modify these settings.
Step 6: Validate AI Settings
When settings are submitted:
Submitted Value ↓ Validation ↓ Sanitization ↓ Storage
Use appropriate validation for each data type.
For example:
Boolean values
Integers
URLs
Text
Model identifiers
API credentials
should not all be handled identically.
Step 7: Create an AI Service
Centralize AI-related business logic in an AI service.
For example:
class MyPlugin_AI_Service { public function generate( $input ) { // AI workflow. } }
A feature can then call:
Feature ↓ AI Service ↓ API Client ↓ Provider
This prevents AI communication from being duplicated across multiple features.
Step 8: Create an API Client
The API client should handle provider communication.
Its responsibilities can include:
Endpoint construction
Authentication
HTTP headers
Request body
HTTP request
Timeout handling
Response retrieval
Provider errors
For example:
AI Service ↓ API Client ↓ WordPress HTTP API ↓ External AI API
This separation makes the integration easier to maintain.
Step 9: Use the WordPress HTTP API
WordPress provides HTTP API functions for communicating with external services.
A simplified request can use:
$response = wp_remote_post( $endpoint, array( 'headers' => $headers, 'body' => $body, 'timeout' => 30, ) );
The exact request depends on the AI provider's current API requirements.
After the request, the plugin should check for HTTP and transport errors before processing the response.
Step 10: Prepare the Request
An AI API request commonly contains:
Authentication
Headers
Model
Instructions
User input
Configuration
Output requirements
Conceptually:
POST AI Endpoint Authorization Content-Type Request Data ├── Model ├── Instructions ├── User Input └── Output Configuration
Keep provider-specific request formatting inside the API client.
Step 11: Validate User Input
Never send arbitrary input directly to an external API without considering validation.
A safer workflow is:
User Input ↓ Validate ↓ Sanitize Where Appropriate ↓ Build Request ↓ AI API
The exact processing depends on the input type.
For example:
Plain text
HTML
URLs
IDs
Email addresses
Structured data
may require different handling.
Step 12: Design the Prompt
The prompt determines how the AI should process the input.
A simple prompt might be:
Write a product description.
A more structured prompt might be:
Task: Create a concise product description. Context: The information comes from a WooCommerce product. Rules: - Use only supplied information. - Do not invent specifications. - Focus on product benefits. - Use clear language. Output: Return only the description.
Clear instructions can make the output easier to process.
Step 13: Separate Trusted Instructions From User Input
AI integrations may process content from users, customers, documents, or WordPress posts.
Treat such content as untrusted data.
A useful conceptual structure is:
Trusted Plugin Instructions + Website Context + Untrusted User Input ↓ AI Request
This distinction is important for reducing prompt-injection risks.
Step 14: Send the API Request
The complete request flow can look like:
User Action ↓ Permission Check ↓ Nonce Check ↓ Input Validation ↓ Prompt Construction ↓ API Request
For public-facing features, additional authentication and rate limiting may be necessary.
Step 15: Handle HTTP Errors
External APIs can fail.
Possible errors include:
DNS/network problems
Timeout
Invalid credentials
Invalid request
Rate limiting
Server errors
Unsupported models
Provider outages
The plugin should detect these conditions.
For example:
if ( is_wp_error( $response ) ) { // Handle transport failure. }
The exact error handling should depend on the feature and provider.
Step 16: Check the HTTP Status
A response can exist even when the request failed.
Therefore, check the HTTP response status before treating the response as successful.
Conceptually:
HTTP Response ↓ Status Check ↓ Success? ┌────┴────┐ Yes No ↓ ↓ Parse Error
This prevents failed API responses from being processed as valid AI output.
Step 17: Parse the API Response
After receiving a successful response, decode it according to the provider's response format.
For JSON responses, the workflow can be:
Raw Response ↓ Decode JSON ↓ Validate Structure ↓ Extract Required Data
Do not assume that every response contains the expected field.
Step 18: Validate AI Output
AI output should be validated before it is used.
Suppose the plugin expects:
{ "title": "Example", "description": "Example description" }
The plugin should check:
Is the response valid?
Is the expected structure present?
Does the title exist?
Is the description a string?
Is the content within acceptable limits?
If validation fails, the plugin should handle the failure safely.
Step 19: Sanitize and Escape Output
AI-generated content should be handled according to its destination.
For example:
AI Output ↓ Validate ↓ Sanitize if Required ↓ Store / Escape for Display
If HTML is intentionally allowed, use appropriate WordPress sanitization.
Do not assume AI output is safe merely because it came from an AI provider.
Step 20: Add WordPress Permission Checks
AI features should respect WordPress capabilities.
For an administrator-only feature:
Request ↓ Current User ↓ Capability Check ↓ AI Processing
For public features, the plugin may need a different authorization strategy.
Permissions should be checked before expensive external API requests whenever practical.
Step 21: Use Nonces Where Appropriate
For WordPress admin forms and applicable AJAX requests, use nonce verification to help protect against unauthorized requests.
A typical workflow is:
Request ↓ Nonce Verification ↓ Capability Check ↓ Input Validation ↓ AI Request
A nonce does not replace authorization. Capability checks and other controls remain important.
Step 22: Add API Timeouts
An external AI request should not be allowed to wait indefinitely.
For example:
WordPress ↓ AI API ↓ Timeout ↓ Graceful Failure
A reasonable timeout should be selected based on the expected operation.
Long-running tasks may be better handled asynchronously.
Step 23: Add Retry Handling
Temporary failures may be recoverable.
For example:
AI Request ↓ Temporary Failure ↓ Retry Check ↓ Retry
However, not every error should be retried.
Invalid credentials and malformed requests generally require configuration or code changes rather than repeated requests.
Step 24: Implement Rate Limiting
AI APIs can impose request limits, and your plugin may also need its own limits.
For example:
User Request ↓ Rate Limit Check ↓ Allowed? ┌────┴────┐ Yes No ↓ ↓ AI API Reject
Possible limits include:
Requests per minute
Requests per hour
Requests per user
Requests per IP
Daily limits
Feature-specific limits
Step 25: Add Caching
Caching can prevent unnecessary AI requests.
Without caching:
Request ↓ AI API ↓ Result
With caching:
Request ↓ Cache ├── Hit → Result └── Miss → AI API ↓ Cache ↓ Result
Caching can improve performance and reduce API usage.
Step 26: Design AI Cache Keys
A cache key should distinguish between materially different requests.
It may depend on:
Feature + Input + Model + Prompt Version + Relevant Settings
If the prompt or model changes, the old cached result may no longer be appropriate.
Step 27: Use Background Processing
AI tasks involving large datasets should not necessarily run during a normal page request.
For example:
1,000 Products ↓ Queue ↓ Background Processing ↓ AI API ↓ Save Results
Background processing can help prevent:
PHP timeouts
Browser timeouts
Long admin requests
Poor user experience
Step 28: Track Background Job Status
For bulk AI operations, show useful progress.
For example:
AI Processing Completed: 420 Remaining: 580 Failed: 8
Useful statuses can include:
Pending
Processing
Completed
Failed
Cancelled
Step 29: Monitor API Usage
AI integrations can benefit from usage monitoring.
Useful metrics include:
Request count
Error count
Average response time
Feature usage
Rate-limit events
Estimated consumption
A plugin can provide an admin dashboard such as:
AI Usage Total Requests: 2,840 Successful: 2,771 Failed: 69
The exact metrics depend on what the provider makes available.
Step 30: Control AI API Costs
Uncontrolled API requests can increase costs.
Use techniques such as:
Caching
Request limits
Input-size limits
Output-size limits
Duplicate-request prevention
Background processing
Processing only changed content
Appropriate model selection
For example, instead of generating a description every time a product page opens:
Product Page Load ↓ AI API
generate the content when the product changes:
Product Updated ↓ AI Generation ↓ Save Result ↓ Reuse Result
Step 31: Protect Personal Information
AI API integrations may transmit WordPress data to external services.
Before sending information, ask:
Is this data necessary?
Does it contain personal information?
Can the data be minimized?
Does the provider process the information?
How long should the plugin retain it?
For example:
Customer Message ↓ Data Minimization ↓ AI API
The plugin should avoid transmitting unnecessary information.
Step 32: Consider Prompt Injection
If your plugin sends user-generated content to an AI provider, malicious or unexpected instructions can appear inside that content.
Potential sources include:
Comments
Contact forms
Product descriptions
Documents
Chat messages
Posts
Separate trusted instructions from untrusted content.
For example:
Plugin Instructions ↓ Website Context ↓ User Content
The AI output should also be validated before being used for sensitive operations.
Step 33: Never Let Raw AI Output Bypass Business Rules
An AI response should not directly perform sensitive operations.
Avoid:
AI Output ↓ Delete User
Prefer:
AI Output ↓ Validation ↓ Business Rules ↓ Permission Check ↓ Action
This is especially important for plugins handling users, payments, orders, permissions, or other sensitive data.
Step 34: Integrate AI With WooCommerce
WooCommerce plugins can use AI APIs for:
Product descriptions
Product summaries
Recommendations
Search
Categorization
Alt text
Customer support
Upselling
Cross-selling
For example:
WooCommerce Product ↓ Product Data ↓ AI API ↓ Generated Description ↓ Merchant Review ↓ Save
The merchant can remain in control of the final content.
Step 35: Integrate AI With WordPress Content
AI APIs can also process posts and pages.
For example:
WordPress Post ↓ AI API ↓ Analysis ↓ Recommendations
Possible features include:
Summarization
Rewriting
SEO suggestions
Title generation
Content outlines
Translation
Readability suggestions
Step 36: Build AI Chatbot API Architecture
An AI chatbot can use a layered architecture:
Visitor ↓ Chat Interface ↓ WordPress Endpoint ↓ Validation ↓ Knowledge Retrieval ↓ AI Service ↓ AI API ↓ Response Validation ↓ Visitor
Public chatbot endpoints should receive additional protection against abuse and excessive usage.
Step 37: Add Knowledge Retrieval
If the AI feature needs website-specific information, retrieve relevant information before generating the answer.
For example:
User Question ↓ Search Knowledge ↓ Relevant Content ↓ AI API ↓ Answer
Possible knowledge sources include:
WordPress pages
Posts
FAQs
Documentation
Products
The retrieved content should be appropriately scoped and validated.
Step 38: Use Structured Data When Appropriate
For some workflows, structured AI output is easier to process than free-form text.
For example:
{ "category": "electronics", "summary": "Example summary", "confidence": 0.82 }
The plugin can validate each field before using it.
Structured responses can be particularly useful for:
Classification
Product analysis
SEO metadata
Recommendations
Data extraction
Step 39: Add Human Review
For important content, AI should often generate a draft rather than immediately publishing it.
A useful workflow is:
AI Generation ↓ Preview ↓ Human Review ↓ Edit ↓ Approve ↓ Publish
This provides an additional quality-control layer.
Step 40: Design Provider Abstraction
If you expect to support multiple AI providers, isolate provider-specific code.
For example:
AI Service ↓ Provider Interface ↓ ┌─────────────┬─────────────┐ │ Provider A │ Provider B │ └─────────────┴─────────────┘
The core plugin can work with a common interface.
This makes provider changes easier to manage.
Step 41: Version AI Prompts
Prompts can change over time.
For example:
Prompt v1 Prompt v2 Prompt v3
Tracking prompt versions can help with:
Debugging
Cache invalidation
Reproducibility
Testing
Feature updates
A cache key can include the prompt version.
Step 42: Version Provider Integrations
AI providers can change their APIs and models.
A clean architecture isolates provider-specific implementation:
Plugin Feature ↓ AI Service ↓ Provider Adapter ↓ Current API
This prevents provider changes from affecting every feature.
Step 43: Handle API Provider Changes
AI providers may change:
Endpoints
Models
Request structures
Response structures
Authentication
Usage limits
Your plugin should avoid scattering provider-specific assumptions throughout the codebase.
Centralizing the integration makes maintenance easier.
Step 44: Add Logging
Useful logs may include:
Request status
HTTP status
Error type
Processing duration
Background job failures
Provider errors
Avoid logging sensitive information unnecessarily.
Never store private API credentials in ordinary debug logs.
Step 45: Test the Integration
A WordPress AI API integration should be tested under multiple scenarios.
Successful Request
Verify that:
Input ↓ API ↓ Response ↓ Result
works correctly.
Invalid Credentials
Verify that the plugin shows a useful configuration error.
Timeout
Verify that the plugin fails gracefully.
Rate Limit
Verify that the user receives an appropriate message and that the plugin does not continuously retry.
Invalid Response
Verify that malformed AI output does not break the workflow.
Empty Response
Verify that the plugin handles missing content.
Unauthorized Request
Verify that users without appropriate permissions cannot access protected functionality.
Step 46: Test Performance
AI requests can introduce latency.
Measure:
API response time
WordPress processing time
Database operations
Cache performance
Background job processing
Avoid placing unnecessary AI requests in frequently executed WordPress hooks.
Step 47: Test With API Failures
Do not only test successful API responses.
Test:
Network Failure Timeout 401 403 429 500 Invalid JSON Empty Response Unexpected Structure
The plugin should handle each relevant case appropriately.
Step 48: Document the Integration
Documentation should explain:
AI provider setup
API credential configuration
Required permissions
Available features
Usage limitations
Privacy considerations
Troubleshooting
Error handling
Configuration options
Good documentation reduces support requests.
Step 49: Build a Maintainable AI API Layer
A maintainable architecture can look like:
WordPress Feature ↓ Application Service ↓ AI Service ↓ Prompt Manager ↓ Provider Adapter ↓ WordPress HTTP API ↓ AI Provider
Supporting infrastructure:
Cache Queue Logger Rate Limiter Settings
Each component has a defined responsibility.
Example WordPress AI API Integration Structure
A commercial plugin might use:
my-ai-plugin/ │ ├── my-ai-plugin.php │ ├── includes/ │ ├── class-plugin.php │ ├── class-settings.php │ │ │ ├── AI/ │ │ ├── class-ai-service.php │ │ ├── class-prompt-manager.php │ │ └── class-response-validator.php │ │ │ ├── API/ │ │ ├── class-api-client.php │ │ └── class-provider-adapter.php │ │ │ ├── Cache/ │ │ └── class-cache.php │ │ │ └── Queue/ │ └── class-background-processor.php │ ├── admin/ ├── assets/ ├── languages/ └── uninstall.php
A smaller plugin can use fewer files and simpler architecture.
Common WordPress AI API Integration Mistakes
Mistake 1: Exposing API Keys
Private credentials should remain server-side.
Mistake 2: Sending Requests Directly From JavaScript
Browser-side requests can expose credentials and create additional security risks.
Mistake 3: Trusting AI Responses
AI output should be validated.
Mistake 4: Ignoring API Errors
External services can fail unexpectedly.
Mistake 5: No Rate Limiting
Public AI features can be abused.
Mistake 6: No Caching
Repeated requests can increase costs and latency.
Mistake 7: Running Bulk Tasks in Normal Requests
Large workloads should use appropriate background processing.
Mistake 8: Ignoring Privacy
Data sent to an external provider should be understood and minimized.
Mistake 9: Mixing Provider Code With Plugin Features
Provider-specific logic should be isolated where practical.
Mistake 10: Letting AI Bypass Business Logic
AI should remain within normal WordPress permissions and application rules.
WordPress AI API Integration Checklist
API
Provider selected.
Current API documentation reviewed.
Authentication implemented.
Request format implemented.
Response format understood.
Errors handled.
Timeouts configured.
Security
API credentials protected.
Capabilities checked.
Nonces used where applicable.
Input validated.
Output validated.
REST/AJAX endpoints protected.
Performance
Caching considered.
Duplicate requests avoided.
Bulk processing uses background jobs.
API requests are not made unnecessarily.
Timeouts are handled.
Privacy
Data transmission understood.
Unnecessary personal information minimized.
Provider policies reviewed.
Retention requirements considered.
Reliability
Temporary failures handled.
Rate limits handled.
Invalid responses handled.
Logging available where appropriate.
Retry behavior is controlled.
Why Choose Kaddora?
Kaddora focuses on WordPress plugins, themes, templates, and business-oriented website solutions.
A successful WordPress AI API integration requires more than connecting an endpoint. It needs secure credential management, WordPress-compatible architecture, reliable HTTP communication, response validation, performance controls, privacy awareness, and a useful user experience.
ThemeKaddora works across WordPress-focused areas including:
AI
WordPress plugins
WordPress themes
WooCommerce
SEO
Automation
Analytics
Website templates
Business tools
For developers and businesses building AI-powered WordPress solutions, a structured API integration can make AI functionality easier to maintain, expand, secure, and connect with existing WordPress workflows.
Conclusion
WordPress AI API integration provides a practical way to bring artificial intelligence into WordPress plugins and websites.
The basic concept is straightforward:
WordPress ↓ AI API ↓ AI Response
A production-ready implementation requires much more.
A reliable integration should include:
Secure API credentials
A dedicated AI service
A centralized API client
Input validation
Structured prompts
Response validation
Error handling
Timeouts
Rate limiting
Caching
Background processing
Privacy controls
Usage monitoring
Appropriate WordPress permissions
The architecture should also separate provider-specific communication from the rest of the plugin. This makes it easier to maintain the integration as AI APIs, models, and requirements evolve.
Most importantly, AI should work inside the plugin's existing security and business rules rather than bypassing them.
With a carefully designed API layer, WordPress developers can build AI-powered plugins for content, SEO, WooCommerce, search, customer support, automation, and many other use cases while maintaining control over performance, security, privacy, and reliability.
Frequently Asked Questions
What is WordPress AI API integration?
WordPress AI API integration is the process of connecting a WordPress website or plugin to an external AI service through an API so that WordPress can use AI-powered functionality.
How do I integrate an AI API with WordPress?
A typical implementation uses a WordPress plugin, secure API credentials, the WordPress HTTP API, an AI service layer, request validation, response handling, and appropriate security controls.
Can I integrate AI into an existing WordPress plugin?
Yes. Existing plugins can be extended with AI features by adding an AI service, API client, settings, user interface, validation, and appropriate background processing where required.
Should I call an AI API directly from JavaScript?
Private API credentials should not be exposed in browser-side JavaScript. A server-side WordPress integration is generally more appropriate when secret credentials are required.
How do I protect an AI API key in WordPress?
Keep the credential server-side, protect the plugin settings with appropriate capabilities, and avoid exposing the key through front-end code or publicly accessible source files.
Can WordPress use multiple AI providers?
Yes. A plugin can support multiple providers by isolating provider-specific communication behind a common interface or adapter layer.
How do I handle AI API errors?
Check transport errors, HTTP status codes, provider error responses, invalid responses, timeouts, and rate limits. Provide understandable messages while keeping technical details available for appropriate debugging.
How can I reduce AI API costs?
Caching, request limits, avoiding duplicate requests, controlling input and output size, processing only changed content, and selecting appropriate models can help reduce unnecessary API consumption.
Can I cache AI API responses?
Yes. Caching can reduce repeated requests, improve response times, and reduce API usage when the generated result can safely be reused.
Should AI requests run in the background?
Large or long-running operations such as bulk product generation, translation, or document processing are often better suited to background processing than normal page requests.
Can I use AI APIs for a WordPress chatbot?
Yes. A chatbot can use a WordPress endpoint, AI service, external AI API, and optionally a knowledge retrieval layer.
How do I secure a public AI endpoint?
Use appropriate authentication or access controls, input validation, rate limiting, request limits, abuse protection, and response validation. Public endpoints require additional consideration because they can receive requests from untrusted users.
Why should I create an API client class?
An API client centralizes provider communication. This prevents HTTP and provider-specific code from being duplicated throughout the plugin.
Should AI output be trusted?
No. AI output should be treated as external data. Validate and safely process it before displaying, storing, or using it in application actions.
How can I protect against prompt injection?
Separate trusted plugin instructions from untrusted user or retrieved content, limit what AI output can control, validate generated results, and enforce normal WordPress permissions and business rules.
Can AI directly modify WordPress data?
A plugin can use AI-generated information to assist with data changes, but sensitive changes should pass through validation, permissions, and business rules rather than relying solely on the AI response.
Why choose Themekaddora?
Themekaddora provides lightweight, responsive, SEO-friendly WordPress themes with fast performance, WooCommerce compatibility, flexible customization, accessibility-conscious design, modern templates, regular updates, and professional support—providing a strong foundation for businesses building digital products and product-focused websites.
Comments (0)