Introduction
WordPress websites can attract unwanted activity as they grow. Spam comments, fake registrations, automated login attempts, and suspicious requests can create extra work for administrators and increase security risks.
For business websites, membership platforms, blogs, and WooCommerce stores, this activity can affect everyday operations. Spam submissions may clutter forms, bots may repeatedly probe login pages, and excessive requests can consume server resources.
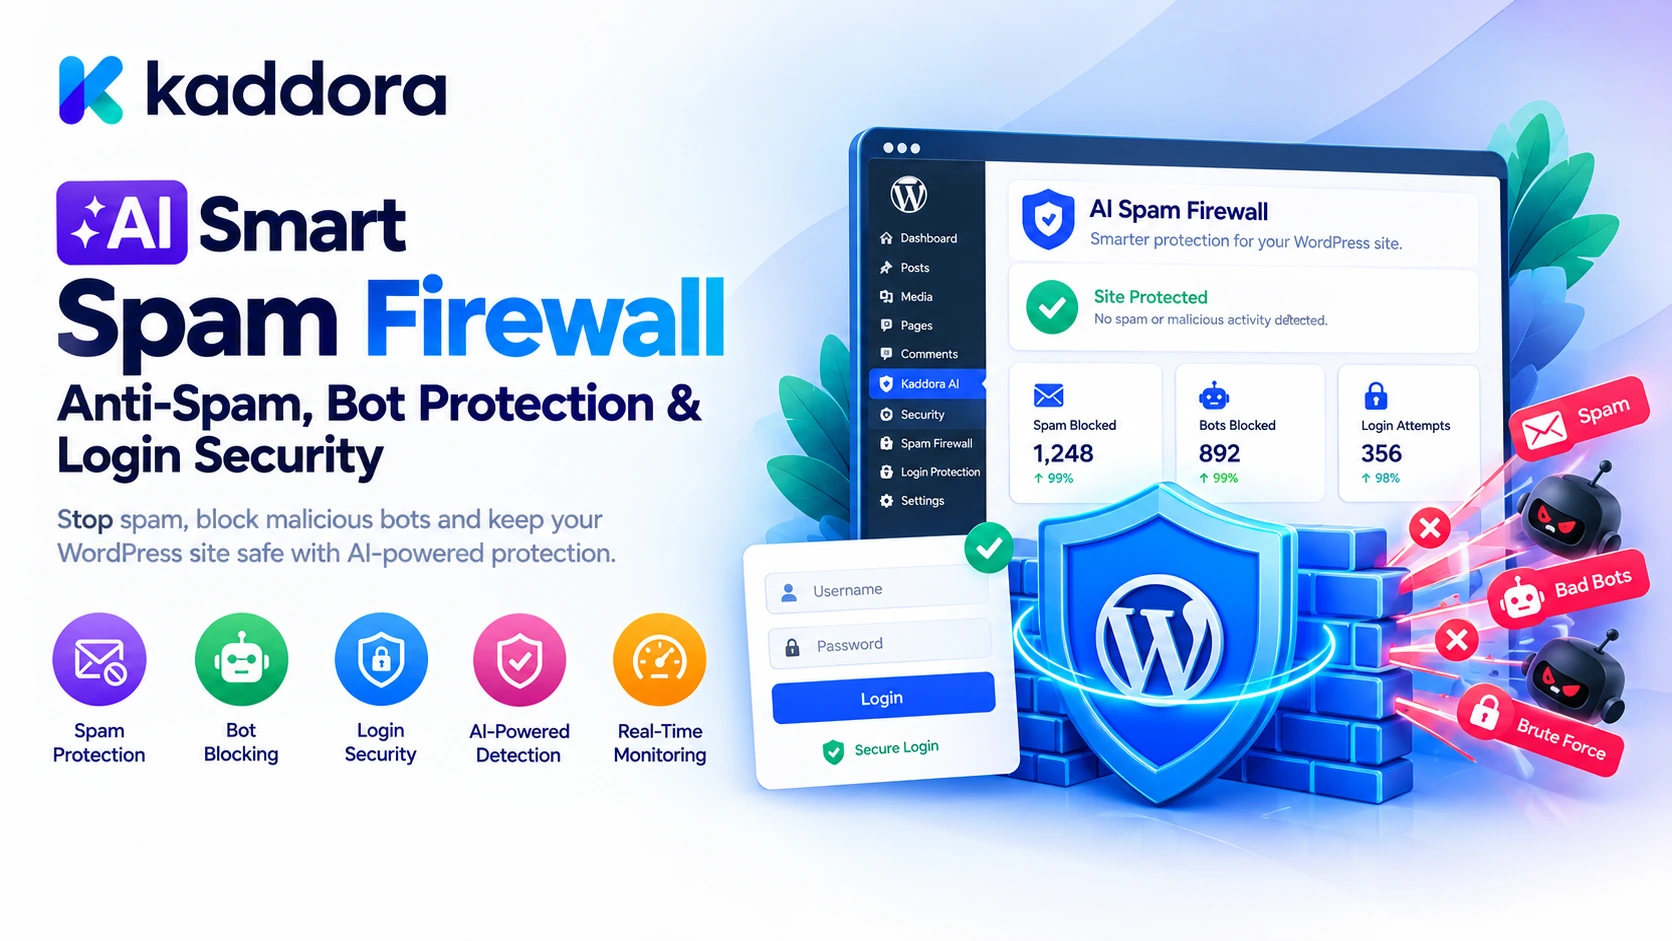
Kaddora AI Smart Spam Firewall – Anti-Spam, Bot Protection & Login Security is designed around helping WordPress website owners manage these risks through a more organized protection workflow.
A typical security process looks like this:
Incoming Request ↓ Request Inspection ↓ Spam and Bot Checks ↓ Login Security Checks ↓ Allow, Challenge, or Block ↓ Monitor Activity
The goal is to reduce unwanted activity while keeping legitimate visitors, customers, and administrators able to use the website normally.
What Is an AI Smart Spam Firewall?
A smart spam firewall helps identify and control unwanted requests using configured rules and supported detection methods. Traditional protection may rely on spam patterns, rate limits, known indicators, or predefined blocking rules. AI-assisted detection may add contextual analysis where implemented.
Depending on the system, relevant signals can include repeated submissions, suspicious login patterns, unusual request frequency, or spam-like form content.
A reliable approach combines AI-assisted analysis with deterministic security controls. The AI should not replace input validation, access permissions, or predictable security policies.
Why WordPress Websites Need Spam Protection
Spam can affect more than blog comments. Depending on a website's features, unwanted activity may target:
Contact and registration forms
Comment sections
Login pages
Newsletter subscriptions
Product reviews
Public search interfaces
WooCommerce forms and account pages
Publicly accessible API endpoints
For example, automated submissions can fill a contact database with fabricated information, while fake accounts can increase moderation work.
A structured protection process can help screen submissions before they are accepted:
Incoming Submission ↓ Input Validation ↓ Spam Detection ↓ Rate and Policy Checks ↓ Accept or Reject ↓ Review Relevant Events
The appropriate controls depend on the website's functionality, risk level, and expected traffic.
What Is Kaddora AI Smart Spam Firewall?
Kaddora AI Smart Spam Firewall is a WordPress-focused security solution centered on anti-spam protection, bot management, and login security.
Depending on the installed version and configuration, its intended protection workflow may cover spam-related activity, suspicious request analysis, login protection, repeated-attempt monitoring, and security event review.
The exact detection methods and available controls depend on the plugin's implementation. Administrators should verify supported features in their installed version before relying on a specific protection mechanism.
The overall objective is to make website security more manageable without creating unnecessary barriers for genuine users.
WordPress Bot Protection
Bots are automated programs that access websites for different purposes. Some are legitimate, including approved search engine crawlers and monitoring services. Others may submit spam, scrape content, test login pages, or repeatedly request resources.
Not every bot is malicious. Blocking automated traffic indiscriminately can interfere with search indexing, uptime monitoring, APIs, and other legitimate integrations.
A sensible bot protection workflow evaluates activity against configured security policies:
Automated Request ↓ Inspect Request Pattern ↓ Evaluate Security Rules ↓ Legitimate or Approved? / \ Yes No ↓ ↓ Allow Challenge or Block
The action should be proportionate to the detected risk. False positives should be reviewed and protection rules adjusted when necessary.
Protect WordPress Login Pages
Login pages provide access to user accounts and administrative functions, making them important security boundaries. Attackers may attempt repeated password guesses or test compromised credentials.
A strong login security strategy includes:
Strong, unique passwords
Multi-factor authentication where available
Appropriate limits on repeated login attempts
Secure account recovery procedures
Monitoring of suspicious activity
Appropriate user roles and permissions
A spam firewall can complement these practices by helping manage suspicious requests where supported. It cannot replace secure account management, software updates, or appropriate WordPress permissions.
Brute-Force Login Protection
A brute-force attack involves repeated attempts to guess a user's password. A protection system can apply rate limits, temporary restrictions, or other configured controls when activity meets defined criteria.
Repeated Failed Logins ↓ Security Rules ↓ Threshold Reached? ↓ Apply Configured Protection ↓ Record Relevant Event
Limits should be carefully configured. Overly strict settings can lock out legitimate users who mistype passwords or share an IP address with other people.
Administrators should test login protections and maintain a reliable recovery process in case their own access is restricted.
Stop Comment and Form Spam
Comment spam often contains irrelevant promotions, suspicious links, or repetitive messages. Form spam can create fake leads, invalid contact details, and unnecessary administrative work.
A spam protection workflow can combine server-side validation, rate limits, honeypot techniques where appropriate, and other supported anti-abuse checks.
AI-assisted analysis may help assess the context of a suspicious submission where implemented. However, unusual wording alone should not automatically be treated as proof of spam, because legitimate users may write short or non-standard messages.
The objective is to reduce unwanted submissions while preserving access for genuine visitors.
AI-Assisted Spam Detection
Spam patterns can change as automated tools vary their messages and behavior. AI-assisted analysis may help interpret patterns that are difficult to identify using simple keyword rules alone.
A combined workflow can look like this:
Request and Content ↓ Input Validation ↓ Rule-Based Checks ↓ AI Analysis, Where Available ↓ Application Policy ↓ Accept, Challenge, or Block
AI can contribute to detection, but trusted application code should make the final decision according to established policies. The model should never be allowed to bypass access controls or modify security settings without authorization.
Reduce Suspicious Registrations
Websites that allow account registration may receive repeated or fabricated signups. These can clutter user lists, reduce subscriber-list quality, and increase moderation work.
Possible safeguards include email verification, sensible rate limits, account approval where appropriate, and monitoring of repeated registration activity.
A smart protection workflow may help flag patterns that deserve further review where supported by the plugin.
Avoid rejecting users solely because they share an IP address or device signal. Families, offices, schools, and mobile networks can legitimately share connections.
Protect WooCommerce Websites
WooCommerce stores handle customer accounts, orders, checkout operations, and other important business functions. Automated abuse may target login and registration forms, product reviews, public endpoints, and other exposed interfaces.
A security plugin should complement WooCommerce's existing validation and security controls rather than interfere with normal purchases.
Test the complete customer journey after configuring protection:
Browse Products ↓ Add to Cart ↓ Login or Checkout ↓ Complete Order ↓ Receive Confirmation
Aggressive blocking rules can disrupt customers or integrations. Verify cart, checkout, account recovery, and payment-related workflows carefully before deploying broad restrictions.
Firewall Protection and WordPress Security
A firewall filters requests according to security rules, but its protection depends on where and how it operates.
A WordPress plugin may inspect requests that reach the application. It should not automatically be assumed to provide the same network-level protection as a hosting firewall, reverse proxy, or web application firewall operating before requests reach WordPress.
A layered setup can look like this:
Internet Traffic ↓ Hosting or Network Protection ↓ Web Server ↓ WordPress Security Controls ↓ Application Permissions ↓ Website
These layers can complement one another when configured compatibly.
Monitor Security Activity
Security protection becomes easier to manage when administrators can review relevant events. Depending on the plugin's logging capabilities, useful information may include the event time, activity category, action taken, and reason for review.
Logs should be protected from unauthorized access and should not store passwords, API keys, session tokens, or other secrets. Collect only the information needed for security monitoring, and establish a reasonable retention policy.
Security logs can help identify repeated attempts and false positives, but logging is not a substitute for prevention or authorization checks.
How to Use Kaddora AI Smart Spam Firewall
The exact interface depends on the installed plugin version. A typical implementation workflow includes:
Step 1: Install the Plugin
Go to WordPress Dashboard → Plugins → Add New → Upload Plugin. Upload the Kaddora AI Smart Spam Firewall ZIP package, then install and activate it.
Step 2: Review Available Settings
Open the plugin's settings or security dashboard and review the available anti-spam, bot protection, and login security controls.
Step 3: Configure Protection
Enable controls appropriate to the website's needs. Understand how blocking, rate limits, and login restrictions may affect regular users and external integrations.
Step 4: Test Normal Activity
Test login, registration, comments, contact forms, and WooCommerce checkout where applicable.
Step 5: Review Events
Use the available reports or logs to investigate suspicious activity and possible false positives.
Step 6: Adjust and Maintain
Refine settings based on observed behavior. Keep WordPress, themes, and plugins updated, and review protection after major website changes.
WordPress Security Best Practices
Use strong authentication. Require unique passwords and consider multi-factor authentication for privileged accounts.
Keep software updated. Apply security updates to WordPress, plugins, themes, and server components through a controlled maintenance process.
Apply least privilege. Give users only the capabilities their roles require, and regularly review administrator accounts.
Validate input server-side. Never rely exclusively on frontend JavaScript to validate form submissions or other requests.
Use appropriate rate limits. Limit repeated requests on exposed forms and login interfaces without disrupting genuine traffic.
Maintain tested backups. Backups provide a recovery path after accidental changes or security incidents.
Test configuration changes. Verify important site functions after enabling or changing security rules.
Common Spam Firewall and Login Security Mistakes
Blocking every bot: Legitimate crawlers and integrations may also send automated requests.
Relying only on AI: Combine contextual analysis with rules, validation, and access controls.
Using weak passwords: Bot protection cannot compensate for poor account security.
Ignoring false positives: Overly aggressive rules can block legitimate users.
Failing to test WooCommerce: Checkout and account workflows must remain functional.
Leaving software outdated: Security controls do not eliminate vulnerabilities in outdated components.
Collecting excessive logs: Store only the information needed for security review.
Assuming every failed login is an attack: Users can mistype passwords or share connections.
Forgetting backups: No security plugin can guarantee every incident will be prevented.
Treating a plugin as complete protection: Effective security needs multiple layers and ongoing maintenance.
Kaddora AI Smart Spam Firewall Checklist
Before relying on a WordPress spam and bot protection configuration, verify:
The plugin is installed and configured correctly.
Login protection settings match the website's needs.
Forms and comments have suitable spam controls.
Rate limits allow normal traffic.
Legitimate bots and integrations are not blocked unnecessarily.
WooCommerce account and checkout workflows are tested.
User permissions follow least privilege.
WordPress and plugins are updated.
Security events are reviewed where logging is available.
Logs do not expose secrets.
A recovery process exists for accidental lockouts.
Backups are available and tested.
False positives are investigated.
Protection rules are reviewed after website changes.
Why Choose Kaddora?
Kaddora focuses on practical WordPress, WooCommerce, AI, automation, security, and website management solutions for businesses, publishers, developers, agencies, and online store owners.
Spam and suspicious automated activity can complicate the maintenance of a WordPress website. A structured protection approach combines prevention, monitoring, sensible access rules, and ongoing maintenance.
Kaddora AI Smart Spam Firewall – Anti-Spam, Bot Protection & Login Security is designed around helping website owners manage these protection needs. Depending on the installed version and supported features, the workflow may help with spam-related activity, suspicious bot requests, login security concerns, repeated automated attempts, and security event review.
The objective is to strengthen website protection while maintaining a usable experience for legitimate visitors and customers.
Kaddora's broader ecosystem focuses on practical WordPress and WooCommerce solutions. These tools work best alongside strong authentication, regular updates, backups, careful permissions, and responsible monitoring.
Conclusion
Kaddora AI Smart Spam Firewall – Anti-Spam, Bot Protection & Login Security focuses on helping WordPress website owners approach spam and unwanted automated activity through a structured protection workflow.
Spam submissions, suspicious bots, repeated login attempts, and fake registrations can create operational problems and security risks. Appropriate safeguards can help manage these activities without unnecessarily disrupting legitimate users.
A practical strategy combines request inspection, spam and bot checks, login controls, rate limiting, security policies, and monitoring. AI-assisted analysis may contribute to identifying suspicious patterns where supported, but trusted rules, application permissions, regular updates, and tested recovery procedures remain essential.
The core principle is simple:
Reduce unwanted activity, protect account access, and keep legitimate website interactions working smoothly.
Frequently Asked Questions
What is Kaddora AI Smart Spam Firewall?
Kaddora AI Smart Spam Firewall is a WordPress-focused security solution centered on anti-spam protection, bot management, and login security. Exact features depend on the installed version and configuration.
What does a WordPress anti-spam plugin do?
It helps identify and manage unwanted submissions, comments, registrations, or other spam-related activity through supported rules and detection methods.
What is bot protection in WordPress?
Bot protection helps distinguish unwanted automated requests from legitimate website activity and applies suitable controls to suspicious traffic.
Can AI help detect spam?
AI can assist with contextual analysis where implemented. It should complement, not replace, validation, rate limits, and application security rules.
Can Kaddora protect WordPress login pages?
Login protection is part of the plugin's intended focus. Available mechanisms depend on the installed version and its settings.
What is a brute-force login attack?
It involves repeated attempts to guess login credentials. Rate limits, strong passwords, and other authentication safeguards can help reduce this risk.
Can a spam firewall block all malicious traffic?
No. No single plugin can guarantee that every malicious request will be detected. A layered security strategy is more dependable.
Can bot protection affect search engine crawlers?
Yes. Incorrect rules can block legitimate crawlers or integrations, so protection settings should be tested and reviewed carefully.
Does a WordPress firewall replace hosting security?
No. Plugin-level and network-level protections operate at different layers and can complement one another.
Why choose ThemeKaddora?
ThemeKaddora provides WordPress themes, plugins, templates, WooCommerce solutions, AI tools, security products, SEO utilities, automation products, and performance-focused website solutions for developers, agencies, publishers, and businesses.
Comments (0)