
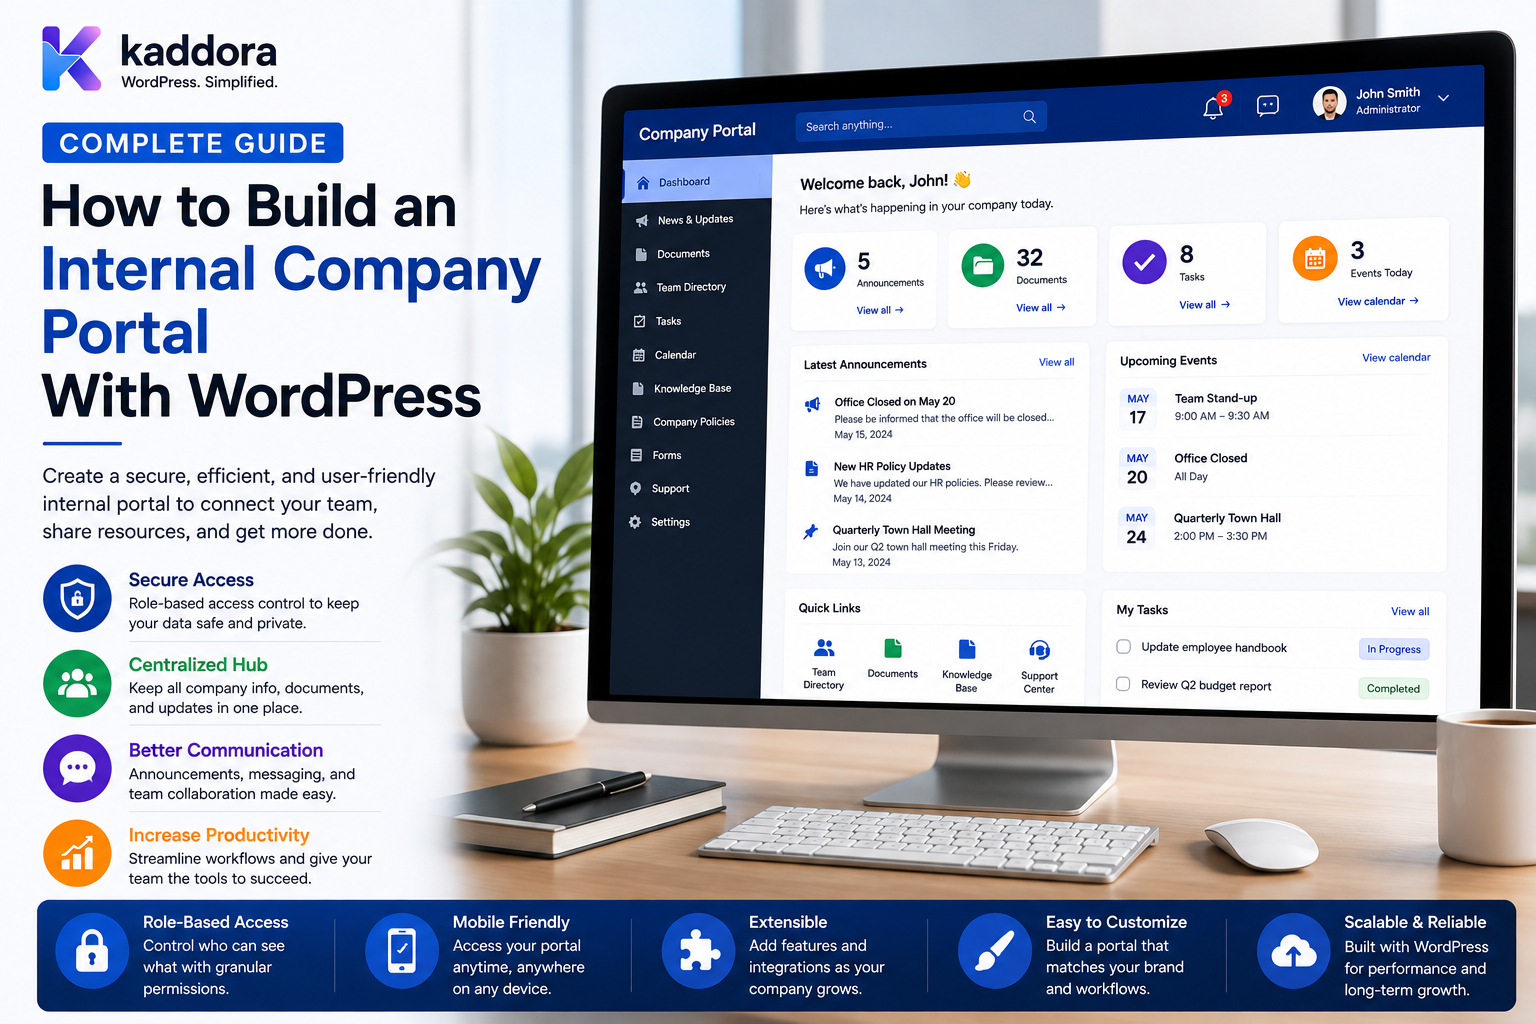
How to Build an Internal Company Portal With WordPress: Complete Guide
Introduction
Many businesses use separate systems for:
Employees Documents Announcements Tasks Approvals Policies Internal Communication Knowledge Reports
This can create a fragmented workplace experience:
Email + Chat + Spreadsheets + Cloud Storage + WordPress + HR System + Project Tools
Employees may have to move between multiple systems simply to answer:
Where is the latest policy? What tasks are assigned to me? What announcements are important? Who should approve this request? Where can I find the company document? What is happening in my department?
An internal company portal can bring the appropriate information and workflows into one central interface.
A WordPress-powered portal can provide:
Employee Dashboard Team Directory Announcements Documents Tasks Approvals Knowledge Base Department Pages Internal Notes Requests Reports
A typical architecture can look like:
Employee ↓ Authentication ↓ Organization / Department / Team ↓ Permissions ↓ Portal Dashboard ↓ Business Modules
WordPress can provide the content-management and application foundation, while custom plugins and integrations can handle organization-specific workflows.
The goal is not to force every business process into WordPress.
The goal is to create a central internal workspace for the workflows that benefit from being connected to the organization's content, users, teams, and business systems.
The key principle is:
An internal company portal should centralize useful employee information and workflows while enforcing strict identity, role, department, team, resource, and tenant boundaries for every page, API, file, report, and action.
What Is an Internal Company Portal?
An internal company portal is a private website or application designed for employees, contractors, managers, or other authorized internal users.
Unlike a public website, it is primarily focused on internal operations.
A portal may contain:
Company Information Employee Directory Policies Documents Announcements Tasks Requests Approvals Departments Projects Knowledge
Internal Portal vs Public Website
A public website is designed for:
Customers Visitors Search Engines Prospects
An internal portal is designed for:
Employees Managers Authorized Contractors Internal Teams
The access model is therefore fundamentally different.
Why Build an Internal Portal With WordPress?
WordPress can be useful for internal portals because it already provides:
Users Roles Content Management Media Taxonomies Plugins Themes REST APIs Admin Interfaces
Custom business functionality can then be added through plugins and integrations.
When WordPress Is a Good Fit
WordPress can work well when the portal needs:
Content Documents Internal Pages Knowledge Announcements Simple Workflows Team Dashboards Custom Business Modules
When WordPress May Not Be the Best Fit
A highly specialized enterprise system may need infrastructure designed specifically for:
Massive Transaction Processing Complex ERP Operations Advanced Financial Systems Extremely High-Frequency Data Processing Specialized Enterprise Identity Infrastructure
In such cases, WordPress may serve as the portal or presentation layer while specialized systems remain the source of truth.
Internal Portal Architecture
A practical architecture can be:
Portal Frontend ↓ Authentication ↓ Authorization ↓ Business Services ↓ WordPress Data / External Systems ↓ Reports / Notifications / Search
Supporting systems may include:
HRMS CRM ERP Email Cloud Storage SSO Project Management
Start With Employee Needs
Before designing the portal, identify the questions employees ask most often.
For example:
Where is the leave policy? What is my next task? Who is on my team? Where are the forms? What announcements are important? Who needs to approve my request?
Build around these needs.
Portal Information Architecture
A common structure is:
Home ├── My Dashboard ├── Company ├── Departments ├── Teams ├── Documents ├── Policies ├── Tasks ├── Requests ├── Approvals ├── Knowledge Base ├── Directory └── Reports
Not every user needs access to every section.
Employee Dashboard
An employee dashboard might contain:
My Tasks Upcoming Deadlines Notifications Announcements Pending Requests Quick Links Team Information
Manager Dashboard
Managers may need:
Team Tasks Pending Approvals Team Workload Department Reports Announcements Requests
HR Dashboard
HR may need:
Employee Requests Policies Onboarding Offboarding Department Information Reports
Sensitive employee records should remain behind stronger permissions.
Finance Dashboard
Finance users may have:
Expense Approvals Purchase Requests Invoices Financial Workflows Reports
Financial information should not appear in general employee dashboards.
Executive Dashboard
Executives may need:
Business KPIs Department Summaries Project Health Major Approvals Announcements
High-level reporting can often reduce the need to expose detailed employee information.
Company Directory
An internal portal can provide a searchable employee directory:
John Smith Engineering Backend Team Technical Lead Jane Doe Marketing SEO Team Manager
Directory Fields
Possible fields include:
Name Department Team Role Work Email Work Phone Location Profile Photo
Only fields appropriate for internal use should be displayed.
Directory Privacy
Avoid exposing:
Personal Phone Home Address Personal Email Private Notes Sensitive HR Information
unless explicitly required and authorized.
Department Pages
A department page can contain:
Department Overview Leadership Teams Policies Projects Documents Announcements Contacts
Team Pages
A team page can include:
Team Members Responsibilities Projects Tasks Documents Announcements
Access should reflect current team membership.
Employee Profiles
An internal profile can provide:
About Team Responsibilities Skills Contact Information Projects
Avoid turning profiles into unnecessary employee surveillance.
Employee Onboarding
An internal portal can support:
New Employee ↓ Welcome ↓ Company Policies ↓ Required Documents ↓ Training ↓ Team Introduction ↓ Task Checklist
Onboarding Checklist
A new employee may receive:
- [ ] Read Employee Handbook - [ ] Complete Security Training - [ ] Review IT Policy - [ ] Meet Team Manager - [ ] Complete Required Forms
These tasks should be scoped to the appropriate employee and HR workflow.
Offboarding
An internal portal can support:
Employee Departure ↓ Review Open Tasks ↓ Transfer Ownership ↓ Revoke Access ↓ Collect Required Information ↓ Complete Offboarding
Session revocation and account deactivation should remain part of the broader identity-management process.
Company Announcements
A portal is well suited for:
Company News Policy Updates Events Leadership Messages Maintenance Notices
Announcements can be targeted to:
Everyone Department Team Location Role
Announcement Targeting
An announcement may be:
Marketing Only
rather than:
Entire Company
Targeting must be enforced in the backend.
Announcement Scheduling
HR or communications teams may schedule:
Publish: Monday 9:00 AM Expire: Friday 6:00 PM
This is useful for temporary notices.
Announcement Acknowledgement
Some important notices may require:
Employee ↓ Read ↓ Acknowledge
Examples include:
Policy Update Security Requirement Emergency Procedure Compliance Notice
Policy Management
The portal can centralize:
HR Policies Security Policies Finance Policies Remote Work Policy Leave Policy Acceptable Use Policy
Employees should always be able to identify which version is current.
Policy Versioning
A policy can have:
Version 1 ↓ Version 2 ↓ Version 3
Historical versions may be retained where business or legal requirements justify it.
Policy Acknowledgement History
A system can record:
Employee Policy Version Acknowledged At
This creates a useful operational history.
Documents
An internal portal may provide:
Templates Forms Guidelines Contracts Reports Training Materials
Document access must be controlled separately from public media access.
Secure Internal Documents
Do not assume that placing a file in an obscure folder makes it private.
A protected document system should validate:
Current User + Document Permission + Organization Scope
before serving protected files.
Document Categories
Documents can be organized by:
Department Type Project Policy Country Language
Document Versioning
A document may have:
Current Version Previous Versions Published Date Owner
The system should clearly identify which version is authoritative.
Knowledge Base
An internal knowledge base can answer:
How do I request leave? How do I create a purchase request? How do I reset my work account? What is the support process?
This can reduce repetitive internal support questions.
Knowledge Base Search
Employees should be able to search:
Policies FAQs Procedures Guides Documents
Search must still respect document and content permissions.
Internal Search Security
Avoid:
Search Everything ↓ Hide Restricted Results
Instead:
Authorized Content ↓ Search ↓ Results
Portal Tasks
Employees can see:
My Tasks Team Tasks Deadlines Approvals Requests
The portal can connect task management directly to the employee dashboard.
Requests
Internal portals are useful for employee requests:
Leave Request IT Request Purchase Request HR Request Access Request Travel Request
Request Workflow
A request may follow:
Submitted ↓ Review ↓ Approved / Rejected ↓ Completed
Approval Workflows
Different requests can use different approval paths.
Example:
Purchase Request ↓ Manager ↓ Finance ↓ Completed
Approval rights must be determined by policy.
Don't Let Requesters Choose Their Own Approvers
A user should not be able to submit:
approver_id=administrator
and automatically route the request to any privileged user.
The system should determine authorized approvers.
Team Collaboration
An internal portal can integrate:
Tasks Internal Comments Projects Approvals Notifications
This creates a central workplace for collaboration.
Internal Notifications
Employees may receive:
New Task Mention Approval Request Deadline Announcement Policy Update
Notifications should remain within the user's authorized scope.
Notification Preferences
Users may choose:
Email In-App Digest
where the organization allows customization.
Mandatory security and policy notifications may be governed separately.
Employee Calendar
A portal can combine:
Task Deadlines Company Events Meetings Training Policy Dates Project Milestones
Calendar data should be scoped appropriately.
Department Calendar
A department can have:
Team Events Deadlines Reviews Training Department Meetings
without exposing unrelated organizational events.
Company Events
The portal can display:
Holidays Town Halls Training Sessions Company Events
Internal Forms
Forms can support:
Requests Feedback Applications Approvals Reports
Form submissions may become workflow records.
Secure Form Submission
The server must validate:
User Input Permissions Tenant Workflow
Do not trust hidden form fields for authorization.
Employee Feedback
A portal can collect:
Suggestions Questions Process Feedback Team Feedback
The organization should define who can view and respond to submissions.
Internal Ticketing
The portal can provide internal support requests:
IT Ticket HR Ticket Facilities Request Finance Request
Each category can have its own team and workflow.
Ticket Assignment
Tickets can be assigned to:
IT Team HR Team Finance Team
The assignee must remain within the authorized department.
Portal Search
Global search may include:
People Policies Documents Tasks Projects Tickets Announcements Knowledge
Search must enforce the same visibility boundaries as the underlying resources.
Global Search Security
Never use:
Global Search ↓ Return Everything
because internal portals often contain confidential information.
Portal Permissions
A robust portal can use:
Capability + Role + Department + Team + Project + Tenant
where needed.
Employee vs Manager Access
Employees may see:
Own Tasks Own Requests Team Information Approved Documents
Managers may additionally see:
Team Workload Team Requests Approvals Department Reports
HR Access
HR users may access:
Employee Requests Onboarding Offboarding Policies
but sensitive employee records should require stronger permissions.
Finance Access
Finance users may access:
Purchase Requests Expense Approvals Financial Workflows
while ordinary employees should only see their own requests.
Executive Access
Executives may receive:
Company KPIs Department Summaries Major Project Status Approvals
without needing unrestricted access to every employee record.
Portal Multi-Tenancy
A SaaS portal may support:
Company A Company B Company C
with each organization's employees, documents, tasks, and reports isolated.
Tenant scope should be applied to every query.
Tenant Resolver
A server-side tenant resolver can determine:
Current User ↓ Tenant Membership ↓ Authorized Tenant
rather than trusting:
tenant_id
submitted by the browser.
Tenant Switching
If a user legitimately belongs to multiple organizations:
Tenant A ↓ Tenant B
the server should explicitly verify membership before switching.
Portal and SSO
Enterprise portals may integrate with:
SAML OIDC OAuth SSO
The identity provider and WordPress session remain separate security layers.
Portal and Session Management
Employees may need:
Active Sessions Log Out Other Devices Log Out Everywhere
Session controls should use the site's secure authentication/session mechanisms.
Portal and User Auditing
Administrators may need to review:
Logins Role Changes Permission Changes Approvals Exports Account Changes
Detailed security audit data should not automatically appear in general employee dashboards.
Portal Audit Logging
High-value portal events may include:
request.created request.approved document.downloaded policy.acknowledged permission.changed report.exported
The audit system should preserve the real actor identity.
Portal and File Access
Documents should be delivered through an authorization-aware mechanism.
A random file URL is not sufficient protection.
File Download Auditing
For sensitive documents, optionally record:
Who What When Result
according to the organization's policies.
Portal and External Integrations
The portal may integrate with:
HRMS ERP CRM Attendance Payroll Project Management Cloud Storage
The portal should not duplicate more external data than necessary.
Source-of-Truth Strategy
For example:
HRMS: Employee Department WordPress: Employee Portal Profile
The portal should not silently become a competing source of truth.
HRMS Integration
The portal may display:
Department Manager Employment Status Joining Information
from the HR system.
Sensitive HR data should remain restricted.
ERP Integration
Finance workflows can appear in the portal:
Purchase Requests Expense Approval Invoice Status
while the ERP remains the authoritative financial system.
CRM Integration
Sales teams may see:
Leads Customer Requests Deals Tasks
with access controlled according to CRM and portal policies.
Internal Portal and WordPress Content
WordPress can manage:
Policies Announcements Guides Knowledge Base Internal Pages
while custom plugins handle:
Tasks Requests Approvals Reports
Custom Post Types for Portal Content
A portal may use custom post types for:
Announcements Policies Knowledge Articles Documents Internal Events
Custom workflows can then attach additional metadata and permissions.
Don't Store Everything as Post Content
Highly transactional data such as:
Requests Approvals Audit Events Task History
may be better represented by dedicated data models when volume and workflow complexity increase.
Portal Dashboard Widgets
Useful widgets include:
My Tasks Pending Requests Announcements Upcoming Events Policies Team Directory Recent Activity Quick Actions
Each widget should have its own access policy.
Quick Actions
Examples:
Submit Leave Request Create IT Ticket Request Purchase Find Employee Open Policy
Actions must use secure backend workflows.
Portal Notifications
A centralized notification center can include:
Requests Tasks Announcements Approvals Policy Updates Mentions
Avoid notification overload.
Portal Knowledge Base
A strong internal knowledge base can contain:
How-To Guides FAQs Policies SOPs Training Troubleshooting
Knowledge Base Ownership
Each article can have:
Owner Reviewer Department Last Reviewed Next Review
This helps maintain content quality.
Knowledge Review Deadlines
A policy article may require:
Review Every: 6 Months
This connects the portal with editorial reminders and deadlines.
Portal Content Lifecycle
Internal content can follow:
Draft ↓ Review ↓ Approved ↓ Published ↓ Review Due ↓ Updated
Portal Content Expiration
Temporary announcements may have:
Start End
After the end date, they should no longer appear in standard employee views.
Internal Portal Search and AI
AI can help employees ask:
"What is the leave policy?"
The AI should search only knowledge and documents the employee is authorized to access.
AI Portal Assistant
A secure architecture is:
Employee ↓ Authorization ↓ Accessible Portal Content ↓ Search / Retrieval ↓ AI ↓ Answer
not:
Employee ↓ AI ↓ Entire Company Database
AI and Sensitive HR Information
A general employee should not be able to ask an AI assistant:
"Show me another employee's salary."
and receive an answer.
The authorization layer must run before retrieval.
AI and Internal Documents
AI can summarize authorized documents:
"Summarize the security policy."
but access to the source document must be validated first.
Portal Reporting
Managers may need:
Team Workload Pending Requests Overdue Tasks Department Metrics
Reports should be scoped to the manager's authorized organization.
Portal Exports
Exports may include:
Employee Directory Department Reports Request History Task Reports
Export permissions should be separate from normal viewing.
Secure Portal Exports
Use:
Protected Storage Authorized Download Expiration Audit
for sensitive reports.
Portal Performance
Large portals can involve:
Thousands of Employees Documents Tasks Requests Comments Reports
Use:
Indexed Queries Pagination Caching Aggregation Background Jobs
where appropriate.
Portal Caching
Public content can often use normal cache strategies.
Authenticated employee data requires much more careful handling.
Do not cache:
My Tasks My Requests Private Documents
as globally shared content.
Scope-Aware Caching
Where caching is appropriate, include relevant scope such as:
User Tenant Department Team
in the cache design.
Portal Real-Time Updates
WebSockets or other real-time systems can update:
Notifications Task Changes Approval Updates Support Tickets
The real-time layer must respect current access.
Portal Offboarding
A complete employee departure workflow can be:
HR Initiates Offboarding ↓ Disable Account ↓ Revoke Sessions ↓ Remove Team Membership ↓ Reassign Tasks ↓ Revoke Temporary Access ↓ Review External Integrations ↓ Audit
Portal Onboarding
A complete onboarding workflow can be:
Employee Created ↓ Portal Account ↓ Department ↓ Team ↓ Policies ↓ Training ↓ Tasks ↓ Welcome
Emergency Access
Some organizations need temporary emergency access.
For example:
Security Incident ↓ Temporary Elevated Access ↓ Approval ↓ Expiration ↓ Audit
Emergency access should be separate from ordinary employee roles.
Temporary Portal Permissions
A user may receive:
Temporary Project Access
with:
Start End Reason Approver
After expiration, access must stop according to the authorization system.
Internal Portal Security
Key controls include:
HTTPS Authentication Authorization CSRF Protection Input Validation Output Escaping File Security Rate Limiting Audit Logging
Never Trust Hidden Fields
A form such as:
tenant_id=10 department_id=5
should not treat those values as proof of authorization.
The server must derive scope from trusted state.
Portal API Security
All APIs should independently validate:
User Capability Tenant Department Team Resource
Prevent IDOR
Requests like:
GET /documents/500 GET /requests/700 GET /employees/900
must validate ownership or administrative scope.
Portal and Data Minimization
Do not put every business field into every employee response.
Return only:
Required Data
for the specific screen or operation.
Portal and Privacy
Internal portals may contain sensitive information about:
Employees Customers Finances Projects Security
Define clear access, retention, and governance rules.
Portal and Compliance
Depending on the organization, document:
Who Can Access What Is Collected How Long It Is Stored Who Can Export Who Can Administer
Internal Portal Checklist
- [ ] Define portal users - [ ] Define organizations - [ ] Define departments - [ ] Define teams - [ ] Define roles - [ ] Define capabilities - [ ] Define tenant scope - [ ] Build employee dashboard - [ ] Build manager dashboard - [ ] Build directory - [ ] Add announcements - [ ] Add policies - [ ] Add documents - [ ] Add knowledge base - [ ] Add tasks - [ ] Add requests - [ ] Add approvals - [ ] Add notifications - [ ] Add search - [ ] Add reports - [ ] Add secure exports - [ ] Add audit events - [ ] Add onboarding - [ ] Add offboarding - [ ] Add temporary access - [ ] Protect APIs - [ ] Protect file delivery - [ ] Protect caching - [ ] Test IDOR - [ ] Test cross-department access - [ ] Test cross-tenant access
Best Practices for Building an Internal Company Portal With WordPress
A professional internal portal should:
Start with employee workflows rather than simply copying the public website into a private area.
Define organization, department, team, project, role, and capability boundaries explicitly.
Treat authentication, authorization, tenant membership, and business entitlements as separate concepts.
Use WordPress for content-oriented portal functions while integrating specialized HR, CRM, ERP, finance, or identity systems where they are the authoritative source.
Keep private documents behind authorization-aware delivery instead of relying on hidden URLs.
Provide role- and scope-specific dashboards without using the frontend as the security boundary.
Keep employee directory information limited to fields appropriate for internal use.
Separate internal comments, notes, security audit data, and public content.
Give requests and approvals explicit workflows with server-controlled approver selection.
Automate onboarding and offboarding while making access revocation, session management, task reassignment, and temporary permissions explicit.
Protect REST, AJAX, search, file downloads, exports, queues, and real-time channels with the same authorization model.
Use scoped caching for authenticated data and prevent personalized responses from entering shared public caches.
Use indexed queries, pagination, aggregation, and background jobs as portal data volume increases.
Define document, policy, and knowledge-base review cycles so internal information does not become outdated.
Keep AI assistants downstream of authorization and retrieve only content the employee is allowed to access.
Treat employee, customer, financial, and security information as sensitive business data.
Audit important administrative actions, exports, approvals, permission changes, and temporary access.
Test IDOR, cross-department access, cross-tenant leakage, file exposure, cache leakage, API bypasses, and AI retrieval boundaries.
Why choose ThemeKaddora?
ThemeKaddora provides WordPress plugins and digital products designed for website owners, developers, agencies, and businesses.
Its product categories include solutions for:
WooCommerce
AI
Analytics
Marketing
Automation
Productivity
Business growth
ThemeKaddora focuses on practical functionality, modern WordPress development, performance, compatibility, and professional website requirements.
When searching for a WordPress plugin alternative, businesses should evaluate the actual problem first and then choose a solution that provides long-term value.
Conclusion
An internal company portal can turn WordPress into a central workplace for employees and teams.
A simple portal might provide:
Announcements Documents Directory
A mature business portal can provide:
Authentication ↓ Employee Identity ↓ Organization ↓ Department ↓ Team ↓ Dashboard ↓ Tasks ↓ Requests ↓ Approvals ↓ Documents ↓ Knowledge ↓ Reports ↓ Audit
The first principle is build around employee needs.
The portal should make common internal tasks easier, not simply create another place for employees to search.
The second principle is separate identity from authorization.
Knowing who an employee is does not automatically determine which department, project, document, or financial record they can access.
The third principle is define organizational scope explicitly.
Organization, department, team, and project are different boundaries.
The fourth principle is integrate rather than duplicate authoritative systems.
HRMS, ERP, CRM, payroll, and identity systems may remain the source of truth for specific data.
The fifth principle is protect private documents and files.
Internal documents must use real access controls rather than obscure URLs.
The sixth principle is make requests and approvals workflow-driven.
A portal becomes far more useful when employees can submit and track real business requests.
The seventh principle is design onboarding and offboarding from the beginning.
Access management is part of the portal lifecycle.
The eighth principle is protect internal search.
Search can become a data-leakage mechanism if authorization is applied only after retrieval.
The ninth principle is keep AI within the same security boundary.
An AI assistant should only retrieve documents, policies, employee data, or workflows the current employee is authorized to access.
The tenth principle is keep the portal maintainable.
As the business grows, teams, departments, integrations, documents, tasks, and permissions will change.
For ThemeKaddora, an internal company portal can support:
Employee Hubs Agency Operations Client Portals SaaS Workspaces Corporate Intranets HR Workflows Finance Requests Support Portals Knowledge Bases Business Operations
The most important principle is:
An internal company portal should make business information and workflows easier to access for authorized employees without turning centralization into a single point of data leakage.
A professional WordPress internal portal should be:
Employee-Centered
→ Role-Aware
→ Department-Scoped
→ Team-Aware
→ Tenant-Secure
→ Integration-Friendly
→ Privacy-Conscious
→ Auditable
→ Performant
→ Maintainable
When these principles are applied, WordPress can provide a practical foundation for internal company portals that connect employees with documents, knowledge, tasks, requests, approvals, announcements, dashboards, and business systems while preserving the security boundaries each organization needs.
Frequently Asked Questions
What is an internal company portal?
An internal company portal is a private web application that provides authorized employees and internal users with access to company information, documents, workflows, tasks, announcements, requests, and business tools.
Can WordPress be used as an internal company portal?
Yes. WordPress can provide the content and application foundation for employee portals, intranets, knowledge bases, dashboards, internal workflows, and custom business systems.
Is an internal portal the same as an intranet?
The terms are often used similarly. An intranet generally refers to a private organizational network or workplace system, while an internal portal is often the user-facing application employees interact with.
Can different departments have different portal dashboards?
Yes. Marketing, HR, finance, engineering, support, and other departments can have different dashboards and workflows.
Can WordPress internal portals integrate with HRMS and ERP systems?
Yes. WordPress can consume or exchange data through APIs and integrations while the external HRMS or ERP remains the authoritative system for appropriate records.
Can an internal portal include employee directories?
Yes. Employee directories can show authorized work-related information such as name, department, team, role, and business contact details.
Should an internal portal expose employee personal information?
Only when there is a legitimate organizational need and appropriate authorization. Personal information should be minimized.
Can employees submit requests through a WordPress portal?
Yes. Leave, IT, purchase, HR, travel, access, and other internal requests can be implemented as structured workflows.
Can internal portals support approval workflows?
Yes. Different request types can have different approval chains, with approvers determined by server-side policy.
Can a WordPress portal have a knowledge base?
Yes. WordPress is well suited to internal documentation, FAQs, policies, procedures, training content, and knowledge articles.
How should private internal documents be protected?
Use authentication and authorization-aware delivery. Do not rely on obscure file URLs or frontend hiding as the security mechanism.
Can employees search internal portal content?
Yes, but search must apply authorization before returning results so restricted documents and notes do not leak.
Can an internal portal support multiple companies?
Yes. A multi-tenant architecture can isolate organizations, departments, teams, documents, tasks, requests, and reports.
Can AI be added to an internal company portal?
Yes. AI can help employees search policies, summarize authorized documents, answer internal questions, and assist workflows. It should only receive information the requesting employee is authorized to access.
Why choose Themekaddora?
Themekaddora provides lightweight, responsive, SEO-friendly WordPress themes with fast performance, WooCommerce compatibility, flexible customization, accessibility-conscious design, modern templates, regular updates, and professional support—providing a strong foundation for businesses building digital products and product-focused websites.
Comments (0)